Clickjacking & UI Occlusion Protection
Open Publisher includes a passive, lightweight security system that protects users from clickjacking and UI redressing scams – attacks where a malicious website frames Open Publisher inside a hidden or transparent layer and overlays it with deceptive UI, tricking users into interacting with the attacker’s content while believing they are using Open Publisher normally.
How It Works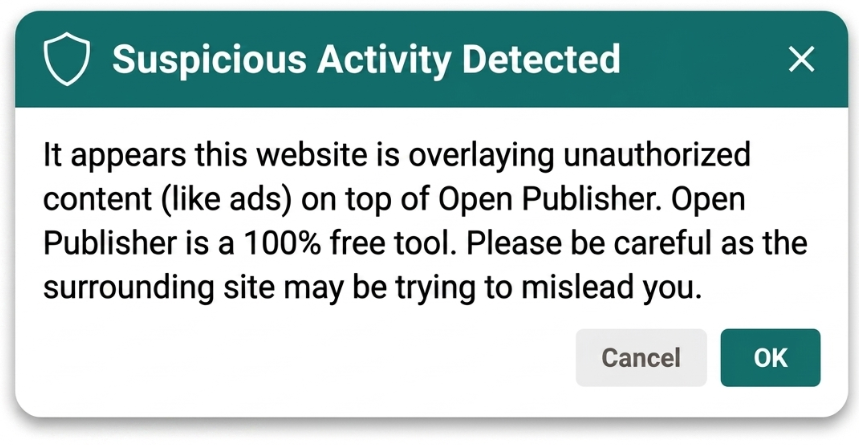
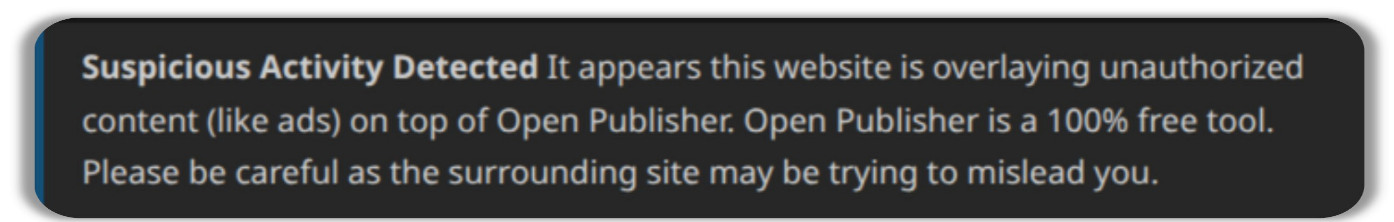
Using the IntersectionObserver v2 (occlusion tracking) API, Open Publisher continuously monitors whether the workspace is being covered by unauthorised content from another frame or website. If an occlusion is detected, a clear in-app warning dialog immediately alerts the user that they may be interacting with a scam.
Key Behaviours
-
No false positives – The system tracks physical pixel occlusion, not domain blacklists, so it never incorrectly triggers against legitimate CMS integrations or creative suite embeds.
-
No forced redirects – The protection does not force browser redirects, avoiding any risk of triggering Google Safe Browsing flags.
-
Graceful fallback – On older browsers that do not support occlusion tracking, the system fails silently via a try-catch – no errors, no broken functionality, just no protection on unsupported browsers.
Authorized Platform Exemptions (Puter.com Cloud Desktop)
Open Publisher is officially accepted and available as a cloud desktop application on Puter.com. Within Puter's browser-based desktop operating system, applications run inside container frames where Puter's native floating window controls (minimize, maximize, close buttons and titlebar chrome) naturally float and hover over the upper boundary of the document workspace.
Under standard occlusion tracking, these floating desktop window controls could be perceived by IntersectionObserver v2 as an external occlusion, potentially causing a false-positive "Suspicious Activity Detected" security alert during normal cloud desktop usage.
To ensure a smooth, uninterrupted user experience while maintaining robust anti-clickjacking protection, Open Publisher incorporates an intelligent, multi-vector platform verification engine (isPuterEnvironment()) that verifies authorized runtime contexts before initializing the occlusion watcher:
-
Ancestor Origins Validation: Verifies window.location.ancestorOrigins against trusted Puter endpoints (puter.com, *.puter.com, and *.puter.site).
-
Parent Frame Referrer Verification: Confirms parent frame document.referrer hostnames originate from verified Puter platforms.
-
Native Hosting Detection: Identifies direct execution hosted under *.puter.site or *.puter.com.
-
Client SDK Telemetry: Detects genuine runtime window.puter and window.parent.puter client SDK objects.
Security Shield Remains Active: This exemption applies exclusively to origin-verified Puter environments. Any unauthorized third-party iframes, malicious wrapper sites, or unverified external overlays remain fully blocked by the Anti Ad-Overlay security shield.